 01
Threats Analysis
Risk assessments in accordance with best practices and other frameworks (e.g. NIST), including recommendations of mitigating the risks.
Liacom provides you confidence knowing that your systems are secures, your teams are always ready, your cyber investments are maximized, and your response to any attack will be most quick and effective
Liacom Systems possesses the knowledge and experience needed to cover all aspects of information security and cyber security at an organization – operational, organizational and technological. thanks to these, Liacom ensures that its customers’ systems are ready and secured.
Liacom’s cyber security innovative solutions are tailor-made to its customer technological and operational needs.
In addition to technological protection, Liacom makes sure that its customers’ team gains the experience they need and trains their workforce and executives to successfully confront cyber threats.
Liacom has a unique expertise in OT and IT environments protection and leads compliance with wide range of regulatory standards, including governmental and defense organizations requirements (e.g. IEC 62443, NERC CIP, ISO, SOX, HIPA, PCI, NIST etc.).
Thanks to all these, Liacom delivers an all-inclusive, organization-wide Cyber protection solution.
01Risk assessments in accordance with best practices and other frameworks (e.g. NIST), including recommendations of mitigating the risks.
 02
Design, test and integrate the essential security architecture and technologies to mitigate risks and integrate within the overall ICT architecture.
 03
Perform internal and external penetration tests (black, white, gray) for infrastructure and applications.
 04
Cyber security and privacy compliance processes for private, public and governmental organizations.
 05
A set of policies, controls, procedures and technologies that work together to protect cloud-based systems, data, and infrastructure.
 06
Preparation of operational procedure for private and public organization for ongoing cyber operations.
 07
Design and implement SOC/CERT for national, sectorial and corporation levels.
 08
Verify and identify supply chain risks including supply chain ICT components clearance.
 09
Ongoing service in response to the legal obligation to appoint a function responsible for information security who manages the entire cyber security and privacy protection in the company. This activity is modularly tailored to the organization's needs: Building and implementing information security procedures, planning and implementing control routines, conducting threat analysis and improving the security system accordingly, identifying cyber security gaps and adjusting solutions, building a training program and implementing the company's operational routine, managing cyber security events in all aspects, ongoing management of documents and systems of privacy protection as well as meeting international standards.
 10
Design a BCP/DRP and the required procedures, to enable recovery of the organization critical business processes and IT systems in an efficient and timely manner in the event of a disaster.
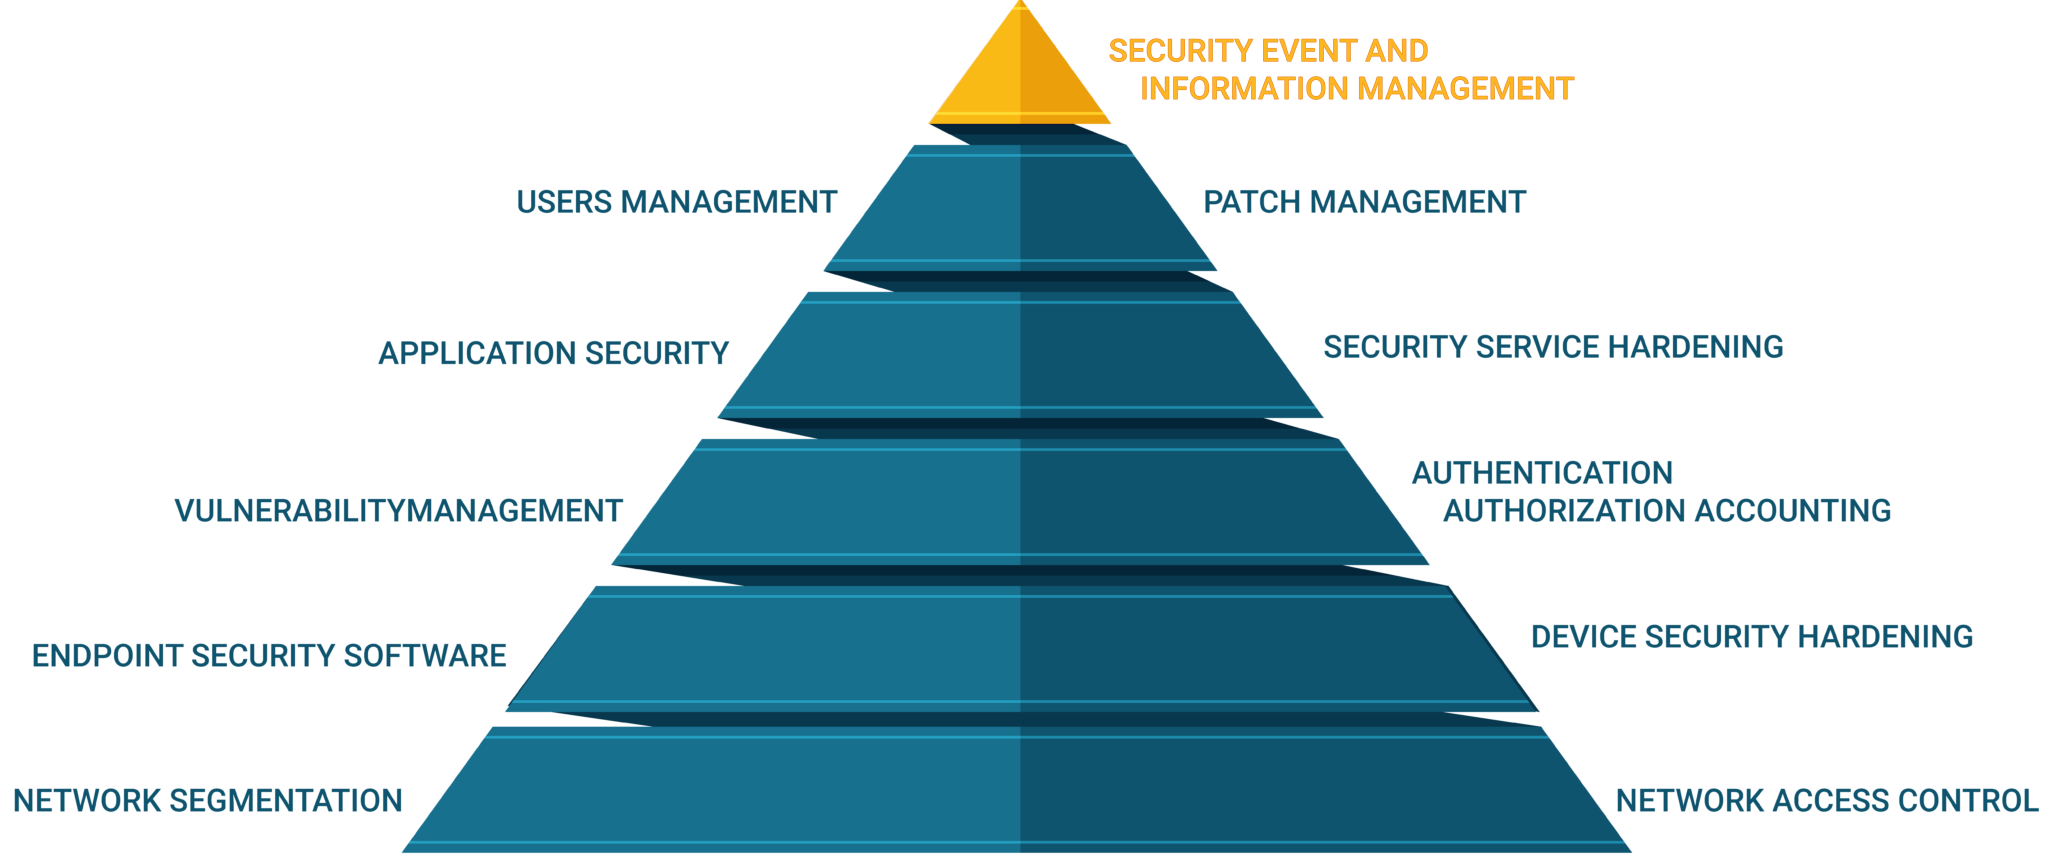
A layered security pyramid covering network segmentation and access control, endpoint and device hardening, vulnerability and identity management, application and service hardening, user and patch management, topped by security event and information management.